>
stark0de
Latest Research
Certified Re-Pwned: escalating all the way up
Renaming the nomenclature: ESC1a, ESC1b, EAB1, and EAB2 At DEFCON 34 we presented five privilege escalation techniques in Active Directory Certificate Services, originally numbered ESC18 through ESC22. After the conference, and after discussing it with Oliver Lyak (the author of Certipy), we did two things: we renamed the techniques so their nomenclature reflects the family they belong to, and we dropped one of them — the original ESC19 — because it does not stand on its own.
How to Accidentally Crash Windows Defender (and Explorer.exe) - Research Summary
Background: Protected Processes in Windows
Windows implements a security mechanism called “Protected Processes” that prevents even administrator-level users from tampering with critical system processes. Many system processes, antivirus solutions, and EDRs use this protection level, including Windows Defender.
Understanding Process Access Rights
When attempting to open a handle to a process using the OpenProcess Windows API function, different access rights can be requested. For protected processes, most access rights are denied by default, even with administrator privileges.
Pwning rConfig: Multiple Vulnerabilities and RCE Chains
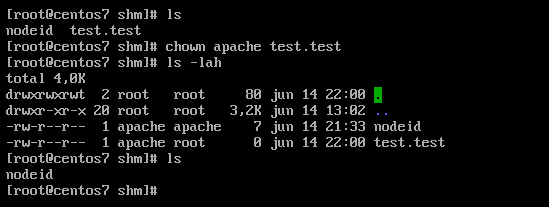
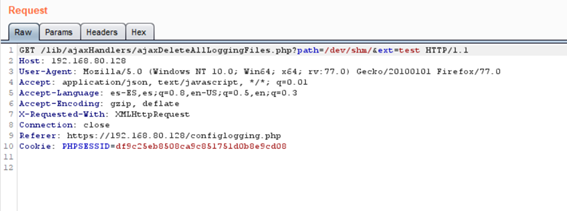
Arbitrary File Deletion:
Location: /lib/ajaxHandlers/ajaxDeleteAllLoggingFiles.php
This vulnerability allows deletion of any file by specifying:
- The file path using the
pathparameter - The file extension using the
extparameter